Cyber Incident Response & Ransomware Recovery for Business
When an account, workstation, server or Microsoft 365 environment is compromised, the first goal is to stop the spread, close breached access and bring the organization back to work in a controlled way. 1iT helps isolate the incident, restore systems, handle identities and harden the environment afterward.
Response is subject to 1iT team availability and service hours (Sun-Thu 8:00-18:00).
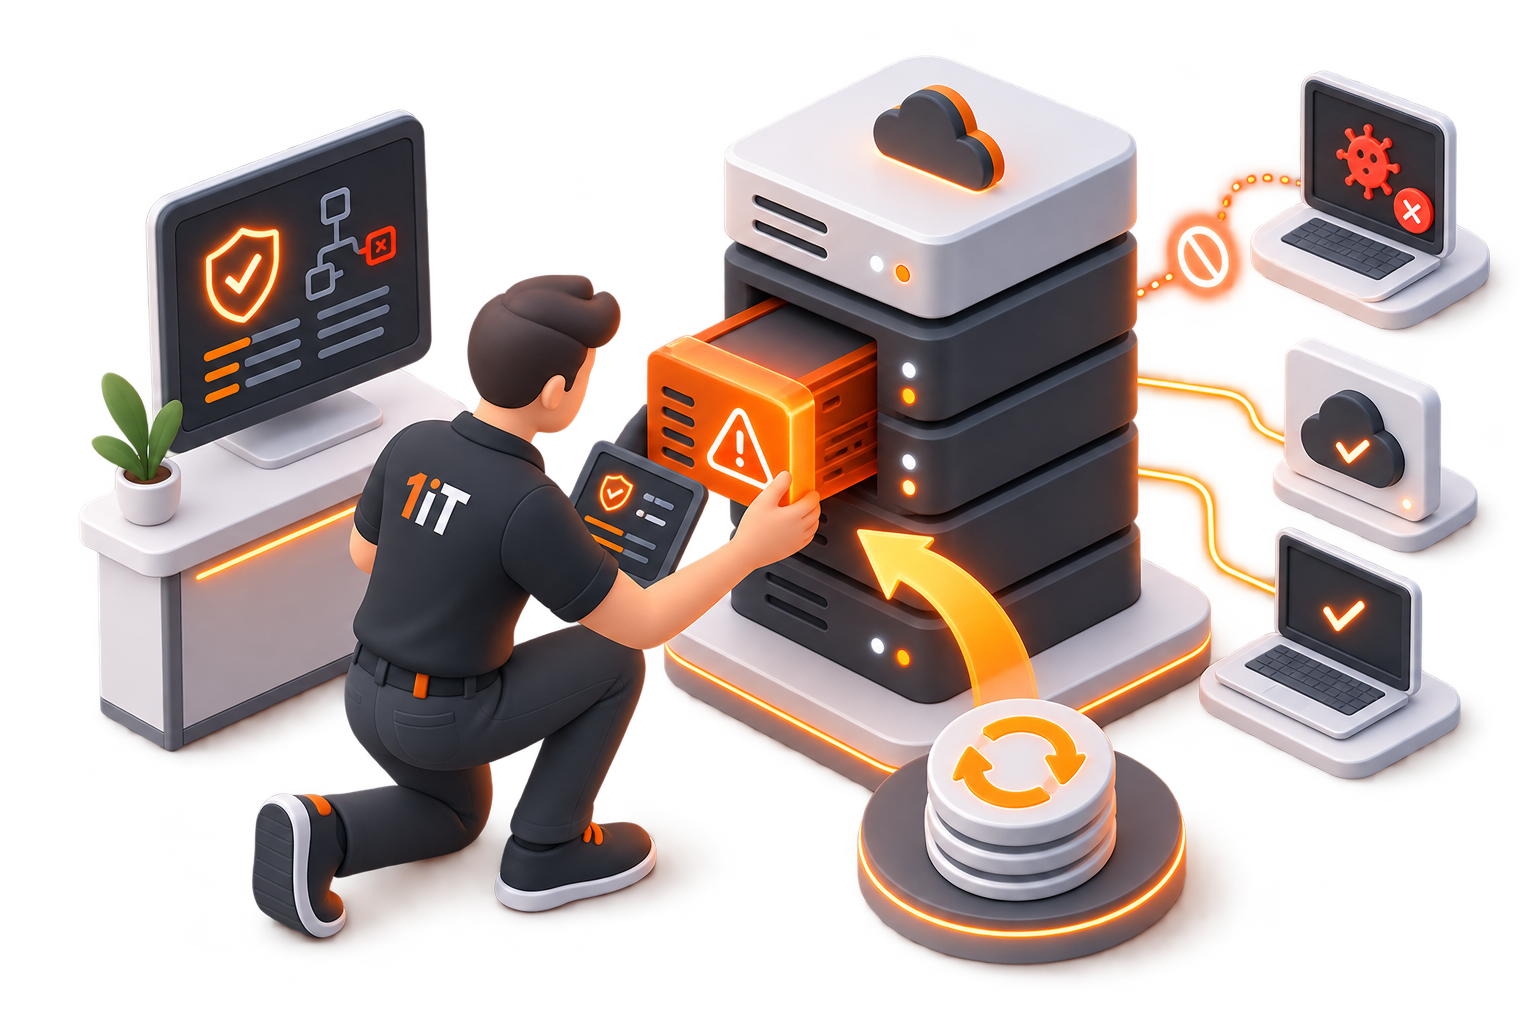
A Cyber Incident Can Start on One Endpoint, One Account, or an Entire System
Files or Servers Were Encrypted
Ransomware
- Files are inaccessible
- A ransom note appeared
- Suspicious encryption activity
- Backup recovery is required
Microsoft 365 or Business Email Was Compromised
Account / email compromise
- A suspicious login was detected
- Mailbox takeover
- Unauthorized forwarding/rules
- Compromised credentials
Suspicious Activity on a Workstation or Server
Endpoint / server
- An EDR detection fired
- Malware
- Unauthorized remote access
- Suspicious processes/activity
The Incident May Have Spread Beyond One System
Broader compromise
- Multiple accounts affected
- Multiple endpoints affected
- Permissions were changed
- Business services impacted
You don't need to know the source of the incident in advance. The first step is understanding what was affected and what's still running.
How an Incident Is Handled - From Containment to Back in Business
01 · Containment & Isolation
Stopping the spread and reducing exposure
- Isolating affected systems
- Closing suspicious access
- Terminating active sessions
- Limiting spread to other systems
02 · Accounts & Identities
Reviewing and closing compromised access
- Account review
- Access reset
- Password and permission changes
- Reviewing users and anomalous permissions
Including Microsoft 365 / Entra ID where relevant.
03 · System Cleanup
Removing the threat and restoring endpoints to a clean state
- Cleaning workstations
- Handling affected servers
- Verification against EDR tooling
- Confirming systems are ready to return to service
In coordination with SentinelOne and EDR.
04 · Recovery & Return to Work
Controlled restoration of data and systems
- Checking recovery points
- Restoring from backup
- Prioritizing critical systems
- Validating integrity after recovery
- Gradual return to operations
Through Cloud Backup, Acronis and Veeam.
05 · Hardening & Monitoring
Closing the gaps the incident exposed
- Permission changes
- Microsoft 365 hardening
- Endpoint security adjustments
- Elevated monitoring after the incident
06 · Investigation & Prevention Plan
Understanding what happened - and preventing the next one
- Technical investigation
- Documenting affected systems
- Identifying failure points
- Remediation actions
- A prevention plan going forward
A Cyber Incident Doesn't Stop at One Product
Endpoints & Servers
Isolation, EDR, cleanup, permissions and restoring systems.
Microsoft 365 & Identities
Users, Exchange, MFA, sessions, permissions and access.
Backup & Recovery
Files, servers, Microsoft 365, recovery points and business systems.
Network & Infrastructure
Scoping the incident, system access and the infrastructure that supports getting back to work.
Incident Response, Cyber Security and Backup Are Not the Same Service
Incident Response Requires Understanding the Whole IT Environment
30+ Years of IT Infrastructure Experience
Long-standing experience managing and rescuing complex IT environments.
Microsoft Security Solutions Partner
Especially relevant when the incident involves identities, email or Microsoft 365 services.
Backup & Recovery Experience
Acronis Platinum alongside existing Veeam and cloud backup capabilities.
Visibility Across the Whole Stack
Endpoints, users, Microsoft 365, backup and infrastructure - under one roof.
Frequently Asked Questions
Is There an Active Incident, or Do You Want to Be Ready Before One Happens?
Active Incident
Detected a breach, ransomware, a compromised account or unusual activity?
073-780-1700Preparing in Advance
We'll review your backup setup, access, Microsoft 365 and your ability to respond and recover, together.
Schedule a Readiness Call